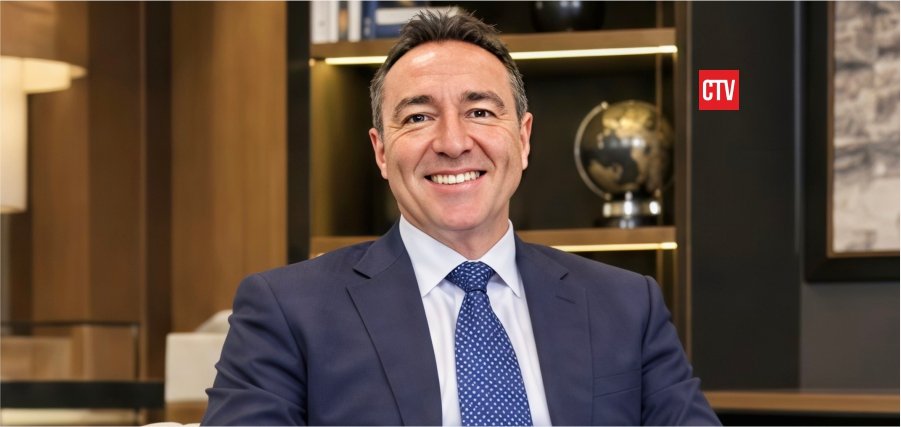
Technology leadership is often measured by what an organisation builds. Andrew Hottes believes it should also be measured by what an organisation can safely sustain.
That distinction has shaped a career spanning more than 25 years in technology, business transformation, cybersecurity, and education, with global CIO experience in Australia, the United Kingdom, Hong Kong, and the United States. Along the way, Andrew has led complex transformations, strengthened cyber resilience, introduced governance disciplines, guided organisations through unprecedented disruption, and helped education institutions approach artificial intelligence with greater responsibility.
Today, as Chief Executive Officer of ISO4, he is focused on a broader challenge: making cybersecurity, AI governance, privacy, risk and compliance practical enough to become part of everyday organisational operations rather than remaining trapped in policies, spreadsheets and annual compliance exercises.
His philosophy is straightforward: “The aim is not to slow innovation down. It is to make the safe path easier than the risky one.”
For Andrew, that principle sits at the centre of modern technology leadership.
From Global Technology to a Human-Centred Mission
Andrew’s professional journey began in the corporate technology environment, where his experiences across international CIO roles exposed him to scale, commercial accountability, transformation and technology risk. Working across Australia, the UK, Hong Kong and the US gave him a broad understanding of how organisations operate and what happens when technology becomes too dependent on individual people instead of strong operating models.
His move into education fundamentally changed that perspective.
In commercial environments, a technology failure can affect revenue, productivity or customers. In schools, the consequences can be far more personal. Technology influences teaching, safeguarding, student wellbeing, family information, assessment and communication. A modern school may resemble a medium-sized enterprise, with cloud platforms, diverse users, connected devices, legacy applications, sensitive information and third-party providers, yet its primary purpose remains education.
That creates a unique responsibility for technology leaders.
Andrew came to believe that technology should enable education rather than force education to work around IT. The question therefore evolved from simply asking whether a technology could be implemented to asking whether it should be implemented, what risks it introduced, who was accountable, and whether the organisation could demonstrate that it was managing those risks responsibly.
That shift—from technology delivery to governance, cybersecurity, privacy, resilience and trust—became a defining feature of his leadership.
Transforming the Digital Foundations of Education
During his time leading digital transformation at a major Australian K–12 school, Andrew inherited a challenge that extended far beyond individual systems. Technology, security, data, user experience and governance all needed to mature together.
The transformation moved the organisation from a reactive IT environment toward one where security and governance were incorporated into technology decisions from the beginning.
The work included infrastructure and core-system modernisation, stronger identity and access controls, network segmentation, security monitoring, vulnerability management and penetration testing. The school also moved away from student BYOD toward centrally managed devices and implemented a whole-of-school management platform designed to improve process consistency, data integrity and organisational visibility.
The results demonstrated that security and user experience do not have to compete.
Managed student devices contributed to an approximately 52% reduction in classroom technology disruptions, while return-to-class times following device issues improved by more than 70%. Infrastructure modernisation also reduced hosting costs while improving resilience and security.
For Andrew, these outcomes reinforced a broader belief: digital transformation is not simply about replacing software. It is about changing how an organisation operates.
His vision was to create an environment where organisations could innovate because their foundations were strong—not despite weaknesses in those foundations.
When Technology Became the Classroom Door
The COVID-19 pandemic provided perhaps the most dramatic test of those foundations.
When schools suddenly moved to remote learning, technology was no longer simply supporting education. In many respects, it had become the classroom door. Students, teachers, and families needed reliable digital access, while technology teams became part of the frontline of educational continuity.
For Andrew, the experience reinforced one of the most important lessons of his career: resilience is built before the crisis.
Trusted relationships, scalable systems, capable people, and sound architecture cannot be manufactured once an emergency begins. Infrastructure decisions can quickly become business-continuity decisions when normal assumptions disappear.
The experience also reinforced his approach to leadership. Leaders will rarely possess every piece of information they would like before a decision must be made. Their responsibility is to provide direction, communicate clearly and give capable people the authority to act.
Andrew therefore views resilience not as a product or a document sitting on a shelf, but as the combination of people, systems, relationships and decision-making capability that allows an organisation to continue functioning when circumstances change.
Making Cybersecurity a Governance Responsibility
One of Andrew’s most significant achievements in education was leading the first Australian K–12 school to achieve ISO/IEC 27001:2013 certification in 2023. Rather than treating certification as an endpoint, he led the transition to ISO/IEC 27001:2022, successfully achieved in 2024. This progression reflected his belief that certification should drive continual improvement, not become a one-time achievement.
ISO/IEC 27001 also reinforced Andrew’s understanding that cybersecurity extends beyond technology. While technical controls matter, effective governance requires organisations to examine ownership, risk, suppliers, policies, incidents, evidence, leadership oversight and continual improvement.
The greater challenge was cultural. In education, stronger controls can initially feel like friction. Andrew therefore focused on connecting these controls to the responsibility of protecting sensitive information about children and families. Over time, security began shaping organisational decisions rather than simply following them.
This thinking underpins his belief that cyber risk belongs at board and executive level. Schools may hold identity, financial, health, pastoral, wellbeing, family and intellectual-property information, including highly sensitive information about children. A serious incident can affect safeguarding, learning continuity, privacy, reputation, finances and community trust simultaneously.
Boards need not become cybersecurity engineers, but they must understand risk appetite, accountability, resilience and evidence. For Andrew, the key question is whether organisations understand their exposure, who owns the risk, and whether controls can be demonstrated to work.
Governing AI Without Blocking Its Potential
The arrival of generative AI has added another layer of complexity to education.
Andrew argues that simply blocking AI is neither practical nor necessarily safe. AI is already becoming embedded in productivity platforms, browsers, educational applications, and vendor roadmaps. A blanket prohibition can create shadow AI, making actual usage less visible and potentially increasing risk.
In 2025, Andrew led the school to become, to his knowledge, the first school globally to achieve ISO/IEC 42001 AI Management System certification. The initiative extended the governance discipline established through ISO/IEC 27001 into AI systems, use cases, risk, impact, accountability, and human oversight.
One of his central principles is that risk lives in the use case, not simply in the application.
An AI platform may present relatively low risk when helping a staff member structure meeting notes. The same platform can become significantly higher risk when processing sensitive student information or influencing a consequential decision.
This thinking also shaped his 2025 book, Classrooms at the Crossroads – The Promise and Peril of AI in Education, which examines both the extraordinary opportunities AI creates for education and the responsibilities surrounding children, privacy, academic integrity and trust.
For Andrew, the answer is neither blind adoption nor blanket prohibition. Good AI governance should create visibility, proportionate assessment, supplier assurance, privacy safeguards, human oversight, accountability and evidence.
The objective is not to slow innovation. It is to make responsible innovation easier.
Leadership Built on Clarity, Accountability and Trust
Andrew does not view innovation and governance as opposing forces. Poor governance, he argues, can actually slow innovation because every proposal must be debated from first principles.
Good governance creates boundaries in advance. It clarifies what can proceed quickly, what requires review, and what risks the organisation will not accept.
His preferred approach is to automate the mechanics while keeping judgement human. When people understand the pathway, lower-risk innovation can move quickly while higher-risk initiatives receive the scrutiny they deserve.
His leadership philosophy rests on clarity, accountability, and trust.
Technology leaders operate between communities with very different needs. Engineers require precision. Teachers need technology that supports learning. Executives need choices and consequences. Boards need assurance without technical theatre. Leadership therefore involves translation.
It also requires avoiding dependency.
Andrew believes a leader should never become the operating system of an organisation. If every important decision, problem and piece of organisational knowledge ultimately reaches one person, that may initially appear to be strong leadership. Eventually, however, it becomes organisational dependency.
That insight helped shape his second book, What Leaders Carry, which explores leadership responsibility, judgement, resilience and the often invisible weight senior leaders accumulate.
His approach extends to mentoring. Through informal mentoring and programmes such as MITIE, he has found particular fulfilment in watching emerging professionals build confidence in cybersecurity and governance and progress into larger roles.
For Andrew, building people is not separate from leadership. It is leadership.
Cyber Maturity Starts With the Foundations
As schools depend on cloud platforms, devices, third-party providers, AI tools, and digital learning systems, Andrew identifies visibility as a challenge.
The attack surface extends beyond the school network to identities, cloud permissions, suppliers, devices, integrations, fourth parties, non-human identities, and AI. Shadow IT and shadow AI complicate visibility.
Strong identity controls, endpoints, vulnerability and patch management, supplier assurance, tested incident response, data governance, and visibility over applications and AI services are essential. These controls must function as a coherent governance system, not disconnected projects.
Andrew warns against confusing buying security with becoming secure. Maturity requires understanding risks, assigning ownership, implementing proportionate controls, collecting evidence, testing controls,s and improving.
The same applies to policy: “A policy that nobody can find is not governance. It is decorative compliance.”
His Andrews Hierarchy of Cyber Needs places technologies and AI above fundamentals. There is little value in debating advanced AI governance when identities are poorly controlled, devices unmanaged, critical data unknown, or disciplines inconsistent.
Andrew calls this the Australian Essential Eight and ISO/IEC 27001 a pincer movement: technical controls on one side, governance, risk and management discipline on the other. Neither suffices alone. Maturity starts with foundations and builds capability.
Turning Experience Into ISO4
These experiences ultimately led to ISO4.
Andrew saw that schools generally understood the importance of cybersecurity, privacy, risk and AI governance. The harder problem was operationalising that understanding.
Evidence could be scattered across spreadsheets, emails, policies, individual staff knowledge, contracts, shared drives, and documents created only when an audit approached.
Having experienced ISO/IEC 27001:2013, the transition to ISO/IEC 27001:2022, ISO/IEC 42001, privacy, supplier governance, cyber transformation, audits and evidence collection from the inside, Andrew recognised an opportunity to make complex governance more practical.
That is the foundation of ISO4: moving governance from a collection of documents and periodic compliance exercises into a working operating model.
As CEO of ISO4, his vision is to make high-quality governance achievable without large compliance teams. ISO4 Schools brings cybersecurity, AI governance, privacy, risk and compliance requirements into practical workflows, assessments, registers, responsibilities, evidence and reporting.
The objective is not simply to digitise an international standard. It is to make the discipline behind that standard usable.
A major part of this approach is distributing governance awareness without fragmenting accountability.
Andrew advocates developing Data Guardians and Technology Risk Ambassadors throughout schools. Data Guardians in teaching and learning, finance, HR, enrolments and wellbeing can understand what information their functions hold, why it is collected, who accesses it and where it flows. Technology Risk Ambassadors can surface new applications, AI tools, supplier changes and emerging risks before they disappear into organisational blind spots.
They do not need to become cybersecurity experts, privacy lawyers or auditors. Their value is proximity to how technology and information are actually used.
The central governance team can continue setting policies, risk thresholds, assurance and escalation, while the Board and executive retain oversight and accountability.
In Andrew’s model: “Distribute awareness. Centralise evidence. Keep accountability clear.”
Preparing for the Next Digital Era
Andrew expects AI to increasingly disappear into the background. Rather than being treated as a separate activity, AI will become part of the applications people already use.
That will require schools to understand not only which products they have approved, but which AI-enabled uses are acceptable, what information systems can access, how outputs are verified and where human accountability remains.
In teaching, AI will challenge assumptions about assessment, authorship, personalised learning and what it means for students to demonstrate understanding. Operationally, it will automate significant amounts of administrative work.
The future will therefore not be determined simply by which AI model becomes most capable. It will depend on whether schools can adopt those capabilities without surrendering privacy, judgement, educational integrity or trust.
Andrew encourages leaders to start with the fundamentals: know critical systems and information, strengthen identity, manage endpoints, understand suppliers, test incident response, maintain accurate software and AI registers, improve data classification and establish AI governance before AI use becomes impossible to see.
Beyond today’s threats, leaders will also need to consider AI-enabled cyberattacks, agentic AI, increasingly complex digital supply chains and eventually post-quantum cryptographic change.
The objective is not to predict every threat. It is to build organisations capable of recognising, governing and responding to risks they did not predict.
A Legacy Measured by What Remains
Andrew’s ambitions for ISO4 over the next five to ten years extend well beyond education. He wants to challenge the belief that strong governance is reserved for large organisations with substantial budgets and dedicated compliance teams. ISO4 is built on a simpler idea: governance administration can be simplified and automated without automating accountability. Its ultimate goal is to shift organisations from asking, “Are we compliant?” once a year to answering, “Are we in control?” every day.
That vision reflects a career recognised through honours including the 2025 iTnews Education Technology Leader of the Year, multiple CIO50 Australia and CSO30 Australia recognitions, iTnews Benchmark Awards, and cybersecurity awards for technology, security and AI governance. His credentials include CISSP-ISSMP, ISO/IEC 27001 Lead Auditor, and ISO/IEC 42001 Lead Auditor. He is also a Fellow of the British Computer Society and a Chartered IT Professional, with further study in Generative AI for Business Transformation through Purdue University and involvement in the Australian Signals Directorate Cyber Security Partnership Program.
Yet Andrew measures leadership differently. For him, true success is whether organisations retain the judgement, capability and confidence to make sound decisions without relying on a single individual. That philosophy connects his books, Classrooms at the Crossroads and What Leaders Carry, and finds practical expression through ISO4.
His guiding principle is clear: “The aim is not to slow innovation down. It is to make the safe path easier than the risky one.” Ultimately, Andrew wants cybersecurity, privacy and AI governance to become so embedded that they no longer feel like programmes—they simply become the way organisations work.